Chinese-Made Zbtlink Routers Ship With Backdoor Vulnerability

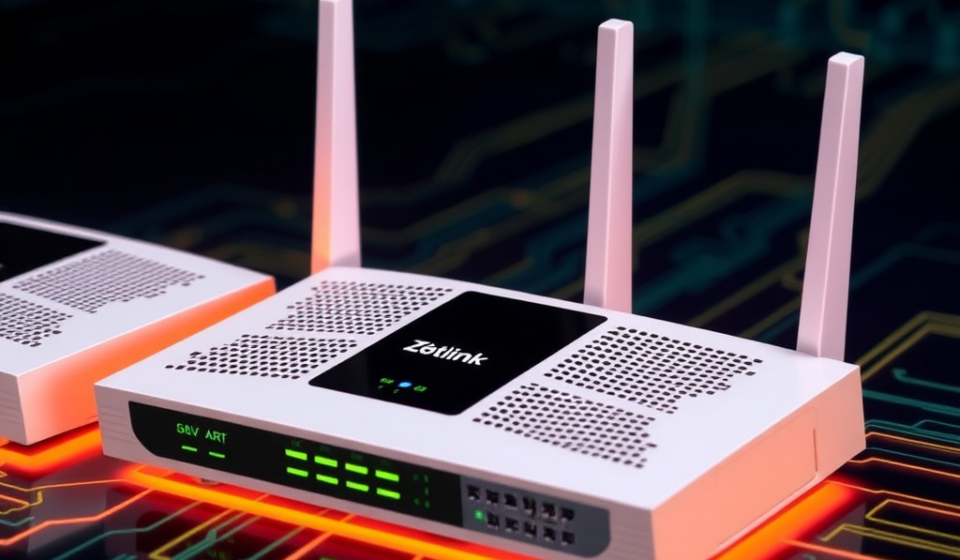
Discovering that Chinese-Made Zbtlink Routers Ship With Backdoor vulnerabilities exposes severe risks to modern networks. Cybersecurity researchers recently found a critical vulnerability in these networking devices. Malicious actors can exploit this flaw to execute unauthenticated root shells. Consequently, thousands of deployed systems face immediate compromise.
As an IT infrastructure practitioner, I immediately recognize the severity of this discovery. Network hardware forms the backbone of digital communications. When foundational devices fail, entire organizational perimeters collapse. Therefore, understanding this backdoor mechanism is vital for maintaining robust defensive postures.
Understanding the Zbtlink Router Vulnerability
Investigating the architecture of compromised networking hardware reveals disturbing design flaws. Vendors sometimes implement hardcoded administrative access points for debugging. Unfortunately, bad actors often weaponize these hidden interfaces. This section explores the mechanics behind the unauthenticated access.
The Anatomy of the Root Shell Backdoor
The core issue lies within firmware binaries that contain hardcoded credentials or hidden listener ports. Specifically, Chinese-Made Zbtlink Routers Ship With Backdoor mechanisms that bypass standard authentication filters. Attackers can connect directly to specific network ports without providing valid credentials.
Once connected, the service grants full root privileges to the remote user. Such unrestricted access allows malicious agents to modify system files, intercept traffic, or pivot deeper into internal corporate networks. Furthermore, traditional perimeter firewalls often fail to inspect internal management services adequately.
Technical Impact on Enterprise Infrastructure
Enterprise environments relying on affordable networking gear face disproportionate risks. A breached router acts as a persistent foothold for advanced persistent threat groups. Moreover, compromised devices frequently participate in large-scale botnets designed for distributed denial-of-service attacks.
IT administrators must prioritize hardware inventory audits immediately. Identifying vulnerable models prevents catastrophic data exfiltration events. For broader context on emerging threats, review insights from The Hacker News report regarding this hardware flaw.
Mitigation Strategies and Network Defense
Defending against supply chain vulnerabilities requires a multi-layered security approach. Organizations cannot blindly trust firmware provided by lesser-known vendors. Instead, proactive hardening measures must be enforced across all edge devices.
First, restrict administrative management interfaces to trusted internal VLANs. Never expose router management ports directly to the public internet. Second, implement robust intrusion detection systems to monitor anomalous outbound traffic originating from gateway devices.
Firmware Updates and Vendor Accountability
Applying patched firmware remains the most effective remediation step. Manufacturers must release security advisories and updated binaries swiftly. However, unsupported legacy models require immediate replacement with enterprise-grade alternatives.
Organizations concerned with hardware integrity should also explore resources within our Cybersecurity category for advanced defense frameworks. Establishing strict vendor risk management policies prevents similar supply chain compromises in the future.
Conclusion
The discovery that Chinese-Made Zbtlink Routers Ship With Backdoor access highlights persistent supply chain risks in global hardware manufacturing. Network administrators must audit device inventories, apply strict access controls, and deploy firmware updates promptly to safeguard critical infrastructure against potential exploitation.